
In September, Delinea published new research on how AI behaves inside companies. Of the 2,254 IT and security leaders it surveyed, 87% said an AI tool or agent had accessed sensitive data beyond what its task needed in the past year. And 55% of organizations said it takes a full day or longer to catch an agent that steps outside its scope.
The report also shows where the gap sits. 99.7% of organizations have a formal policy on what data AI tools and agents can access, but only 51% check access against that policy in real time. In a separate survey of 2,250 non-IT employees, 76% said they have bypassed the required approval to use AI, and 60% said they felt pressured to use AI on sensitive or confidential data when they weren’t sure it was allowed.
Source: Delinea, 2026 Identity Security Report: The AI Enforcement Gap, Sept. 2026.
Policies and approvals say what is allowed. They don’t change what is in the file when someone, or something, gets there anyway. PK Protect protects the file itself.
What a data security platform does
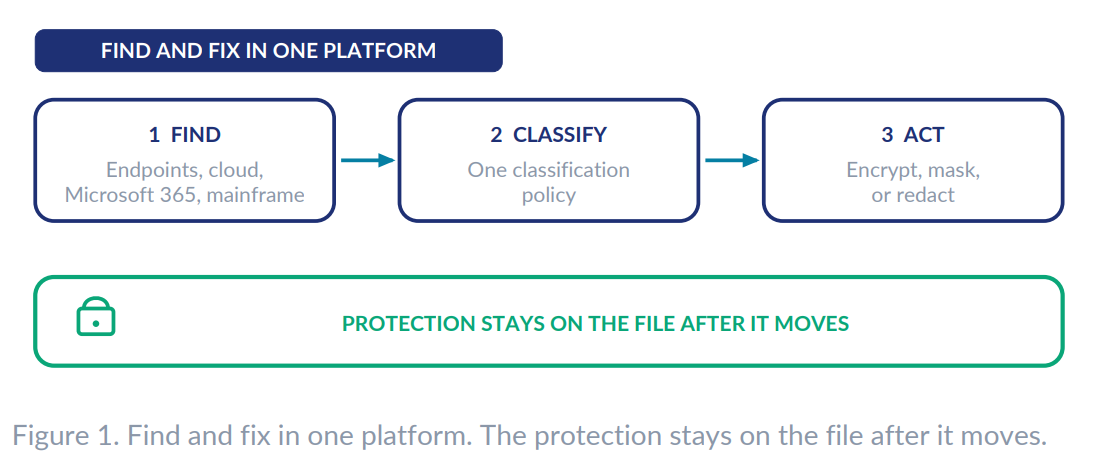
PK Protect finds sensitive data on endpoints, in the cloud, in Microsoft 365, and on z/OS and IBM i mainframes. It classifies what it finds under one classification policy, so the fix matches the data. Then it acts: encrypt it, mask it, or redact it. Part 2 compares this with DLP and DSPM.
What changes about the day-long gap
A late alert tells you what an agent reached. When PK Protect encrypts a file, the protection stays on the file after it moves. An agent that hasn’t been given access to the key can reach the file and still can’t read it. An agent working on a person’s behalf can open what that person can open, which is why controls on the agent still matter.
This covers the file types PK Protect can protect. If someone keeps an unprotected original, that copy isn’t covered. On supported databases, warehouses, and cloud storage, sensitive values are masked instead, so there is no key.